Shadow IT: When staff are quicker than IT
Expand the table of contents
Why can’t the problems solved by bans alone?
How can organisations assess shadow IT in a pragmatic way?
When must the use of shadow IT be stopped immediately?
What does shadow IT reveal about your organisation?
How can managers ensure transparency in the long term?
A Bitkom survey from October 2025 shows just how widespread the problem has become. [1] In 25 per cent of the companies surveyed, private AI applications are demonstrably being used for work-related tasks. A further 17 per cent assume that this is happening. At the same time, only 23 per cent of companies have established binding rules governing the use of AI. Although the figures relate specifically to generative AI, they highlight a fundamental problem: new tools often find their way into everyday working life faster than companies can regulate their use.
Why does shadow IT arise in day-to-day team work?
The main driver behind shadow IT is usually the desire to do one’s job as well as possible. If the approved software does not offer a required function, an interface is missing or the internal approval process takes too long, employees look for alternatives. Cloud applications make this particularly easy for them, as many services can be set up within a few minutes.
There are various triggers for this: for example, a project team may need a digital whiteboard because the client is already using one. A department may develop its own Excel macros to automate recurring tasks. Other employees may use personal AI tools because the company has not yet provided an approved application.
Shadow IT is therefore by no means limited to programmes that are installed secretly. It can also arise within systems that have already been approved. These include, for example, in-house automation tools, databases set up independently, or complex analyses whose inner workings are known only to a few employees.
This becomes problematic, at the very latest, when such solutions become indispensable for key business processes. If the person responsible leaves the company, documentation, access rights or knowledge of technical dependencies may be lacking. What started as a practical way of making work easier has, unnoticed, turned into an operational risk.
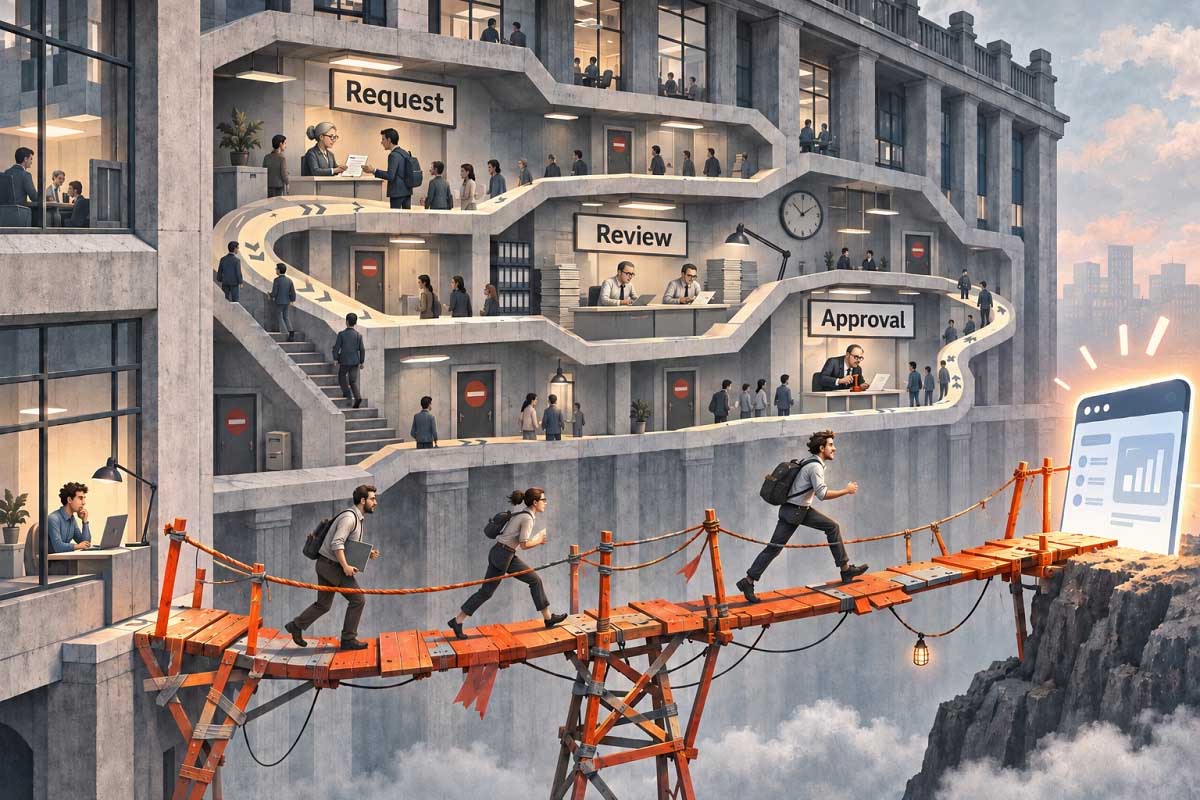
Figure: Shadow IT – also a reflection of the organisation
Why can’t the problems be solved by bans alone?
Organisations have good reasons to regulate the use of software. They must protect personal data, safeguard trade secrets and ensure that business-critical applications function reliably. Without appropriate guidelines, uncontrolled cloud services, private user accounts or insecure interfaces can cause considerable damage.
Nevertheless, blanket bans often fail to address the underlying problem. If a team needs a specific application but there is no official alternative, or the alternative is unsuitable, the pressure to act remains. Employees may then be tempted to resort to using personal devices or accounts. This makes it even more difficult for the relevant IT managers to identify risks.
A ban may therefore be necessary, but it is not sufficient on its own. The key factor is whether the company simultaneously offers a workable solution to meet the actual need.
Managers should be prepared to ask an uncomfortable question: What circumstances led our staff to have to look for their own solution in the first place? Perhaps the approval processes are too lengthy, existing applications are too complicated, or individual requirements have not been taken into account so far. As long as these underlying causes remain, similar problems will arise again.
How can organisations assess shadow IT in a pragmatic way?
One possible approach is a simplified approval process that addresses employees’ actual needs and enables a quick initial decision. To achieve this, responsibilities must be clearly defined between the line department, IT and, where applicable, information security or data protection.
The process should start as simply as possible. Employees need a way to disclose tools they are using or wish to use without having to fill in a lengthy application form. At the same time, it must be ensured that applications posing significant risks are not used without being assessed.
Step 1: Openly identify shadow IT
The first step is to take stock of the situation. Managers can ask their teams to identify regularly used third-party programmes, cloud services, browser extensions and AI applications. The focus should be on the benefits, so that the discussion does not turn into a search for rule violations.
Just a few details are needed for an initial assessment:
- Which tool is being used and what specific problem does it solve?
- What data is processed, stored or transmitted within it?
- Who uses the application and which user accounts are employed?
- Is there already an officially approved tool for the same purpose?
It is important to deal with the results openly. Anyone who discloses justifiable business needs should, as a first step, receive support in finding a secure solution. This does not, however, rule out consequences in the event of deliberate or serious breaches of security requirements.
Step 2: Carry out an initial risk assessment within 48 hours
Prompt feedback is important to ensure that staff do not act on their own initiative again. Companies could therefore aim to make an initial decision within two working days. This timeframe is an organisational suggestion and not a universal requirement for full software approval.
Within this timeframe, the relevant departments should decide how to proceed:
- If the application meets the necessary requirements, it may be authorised for its intended purpose.
- If security issues, data protection requirements or contractual conditions still need to be clarified, further review is required. Until then, use remains restricted to purposes that have already been expressly authorised.
- If the application poses significant risks or contravenes binding regulations, its use is not permitted. In this case, the team requires a suitable alternative.
Such an initial decision can be reached relatively quickly. However, the subsequent review may take considerably longer, depending on the application.
Particularly in the case of cloud services and AI applications, it must be clarified which data is processed, who has access to it and which contractual terms apply. This may include a data processing agreement, appropriate technical safeguards and the legal requirements for international data transfers. [2]
A server location within the EU alone does not guarantee data protection compliance. Conversely, data transfers to third countries may be permissible under certain conditions, such as where an adequacy decision has been made or where suitable safeguards, such as standard contractual clauses, are in place. The specific assessment is the responsibility of the relevant specialist departments.
Step 3: Officially approve suitable solutions
If an application passes the necessary checks, it can be added to the standard software portfolio. It is not sufficient simply to retrospectively authorise its previous use. To ensure reliable operation, responsibilities, access rights and, where applicable, the management of user accounts must be clarified.
Where necessary, private individual accounts should be replaced by centrally managed corporate accounts. Furthermore, clear rules are needed regarding what information may be processed and for which tasks the software is authorised. For example, an AI application might be permitted for editing general texts, whilst the processing of confidential customer information remains expressly prohibited. Such boundaries help employees to use the application safely in their day-to-day work.
If a tool fails the assessment, the company should nevertheless address the original need. A rejection is easier to justify if a suitable alternative is offered or developed jointly.
When must the use of shadow IT be stopped immediately?
A pragmatic approach does not mean, by any means, tolerating every application initially. There are situations in which managers must intervene immediately and involve the relevant departments. This applies in particular when:
- confidential customer information or personal data is transferred to external services without adequate safeguards,
- private user accounts allow uncontrolled access to business-critical systems,
- trade secrets are processed in AI applications, even though their further use or protection has not been sufficiently clarified,
- programmes or browser extensions demand extensive access rights and thereby circumvent security requirements,
- essential business processes are dependent on undocumented applications or individual private access points, thereby giving rise to significant risks.
The urgency with which action must be taken depends on the specific risk. In critical cases, further use must be stopped immediately. If there is a suspicion that data has already been unlawfully disclosed or systems compromised, the designated reporting and security processes must be activated.
For managers, however, this does not mean that they should carry out complex data protection or security assessments themselves. Their role is to identify risks, involve the appropriate departments and ensure that agreed measures are implemented.
What does shadow IT reveal about your organisation?
Anyone who views shadow IT solely as a security issue overlooks an important piece of information: The use of unofficial tools can highlight where the officially designated tools or processes fail to meet actual requirements.
Suppose a department has been using an external project management application for months, even though the company already provides a centralised solution. The obvious reaction would be to ban the additional tool and direct staff to use the existing software. This might resolve the security issue, but it would do little to address the root cause.
Perhaps the central application lacks key functions. It may be that staff are unaware of existing options or require different access rights to collaborate with external partners. Inadequate implementation of the existing software can also lead to teams going their own way.
Such insights are valuable to senior management. They can highlight where investments in software are failing to deliver their expected benefits, where workflows have become unnecessarily complicated, or where decisions are being made too far removed from the requirements of the specialist departments.
However, this does not mean that every unofficial application fulfils a legitimate need. Some tools are used purely out of habit, whilst others solve problems that could just as easily be addressed using the existing software. This is precisely why managers should ask about the specific benefits before deciding on further measures.
Making shadow IT visible is therefore also an opportunity to review one’s own working conditions. The organisation can learn from its employees’ experiences whilst at the same time preventing technical solutions from emerging without adequate oversight.
How can managers ensure transparency in the long term?
A one-off software review will not solve the problem permanently. New applications are introduced, existing tools evolve, and new tasks give rise to further requirements. That is why the question of which applications are needed and which are actually being used should be a regular part of the collaboration between business departments and IT.
Managers can start by asking, at the next team meeting, about the three unofficial tools that currently make day-to-day work the easiest. They can then jointly assess the benefits these applications offer, the risks involved, and whether there are already approved alternatives.
What happens next is crucial. If employees disclose the tools they use, this should lead to a transparent decision. If there is no feedback, or if enquiries get bogged down in internal consultations for weeks on end, the willingness to be open will likely decline again.
A company that provides a binding initial response within two working days at least signals that it takes its teams’ needs seriously. It is then easier to explain why the actual approval process takes longer.
In the long term, therefore, the number of reported shadow IT applications should not be hastily interpreted as a sign of poor IT governance. An increasing number may initially mean that employees are being more open about the tools they use. What is more interesting is what underlying causes come to light, how quickly the company responds, and how many recurring problems can be resolved as a result.
Notes (partly in German):
Are you interested in more perspectives on the digital world of work and other current topics? Then it’s worth taking a look at newsbaron, a German-language online magazine featuring news, guides and articles on technology, business and everyday life.
[1] Bitkom: Employees are increasingly using shadow AI. Press release dated 21 October 2025 based on a survey of 604 companies with 20 or more employees.
[2] European Data Protection Board: Standard contractual clauses – Information on legal safeguards for international data transfers.
Here you can find further information on shadow IT including examples, reasons and implications.
Would you like to support Udo Schluhmeier and discuss shadow IT? Then share this post on social media or within your organisation.
Udo Schluhmeier
Udo Schluhmeier is an editor at newsbaron. He writes practical articles on the digital world of work, artificial intelligence in everyday working life, digital business, start-ups, and IT and technology topics.
His aim is to explain complex developments in an accessible way and to provide readers with practical guidance they can apply in their daily lives. In doing so, he combines current topics with a clear focus on their practical significance for businesses, teams and the self-employed.
On the t2informatik Blog, we share knowledge and experience with people in organisations. We have been developing and modernising software for them since 2012. Pragmatically. ✔️ Personal. ✔️ Professional. ✔️ Get to know t2informatik as your development partner.